Shadow AI detection for Google Workspace and Microsoft Entra ID

Find every unsanctioned AI tool automatically
Surface shadow AI — and the Mail, Drive, Calendar or other critical scopes it was granted — before sensitive data leaves your company.
Stay in control with a modern AI governance and identity solution designed for IT, Security, and Compliance teams to enhance your overall SaaS security posture management.
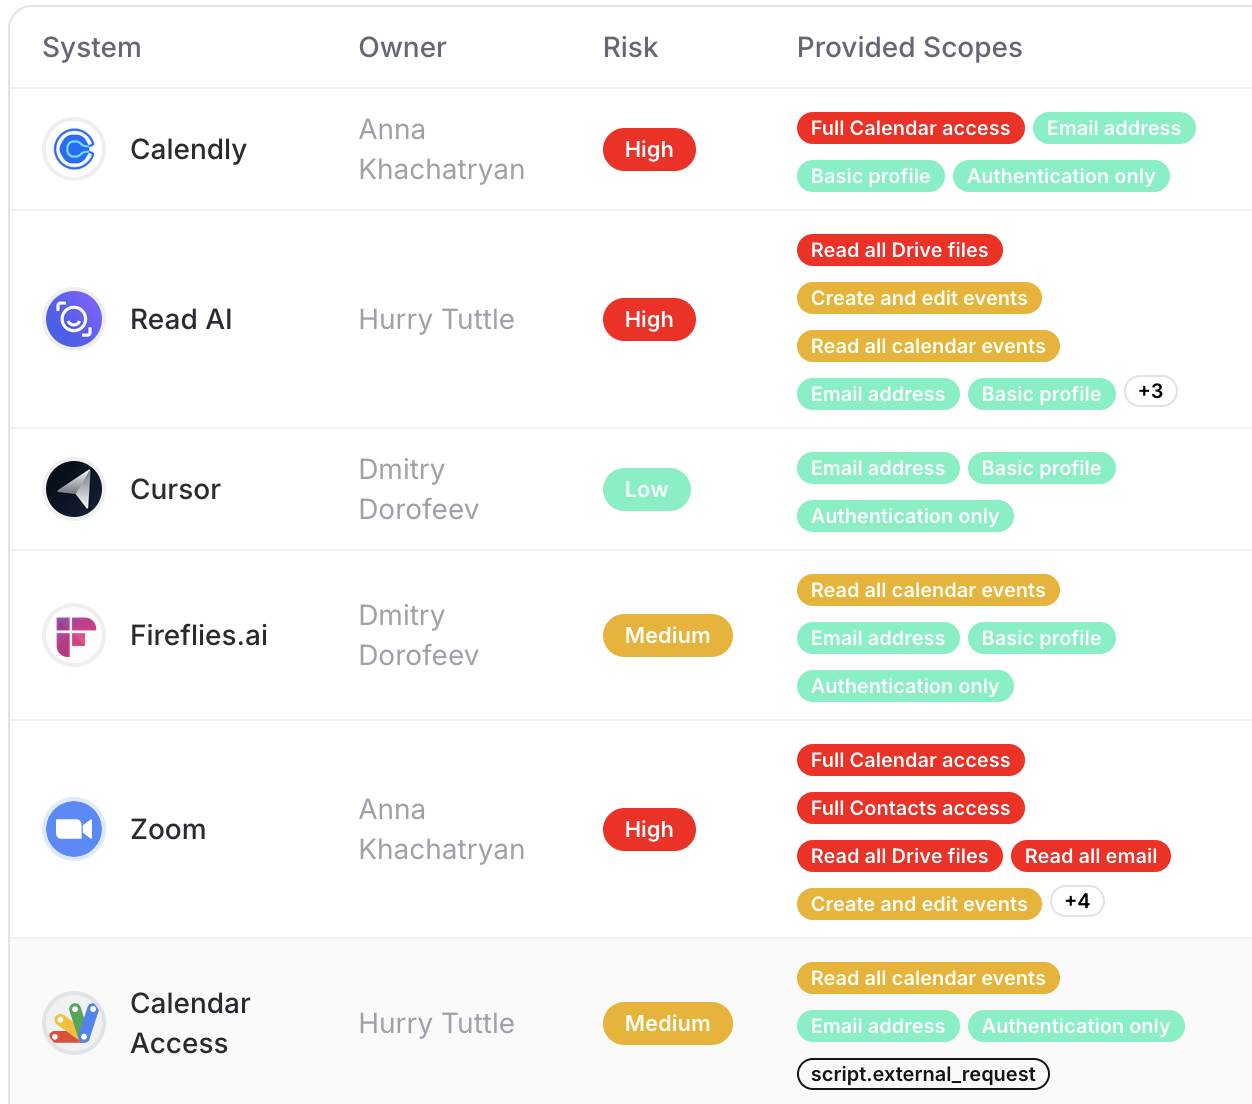
AI tools employees connect via OAuth
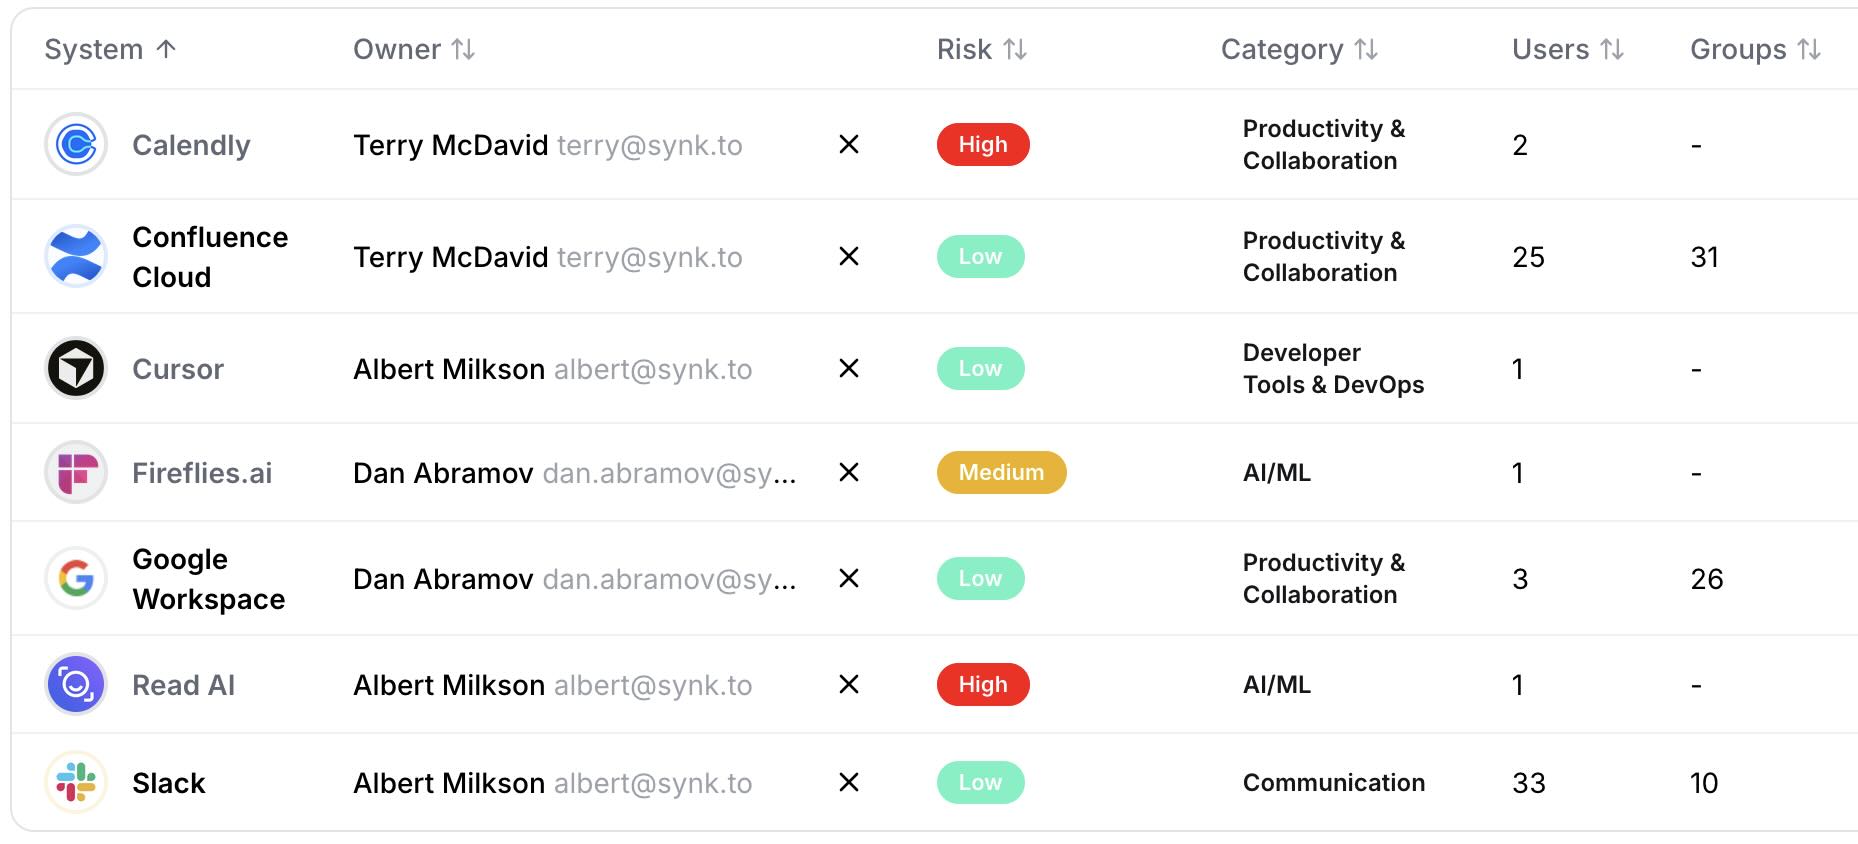
AI note-takers and agents like Otter.ai, Read.ai, Fireflies.ai and Fathom connect to Google Workspace or Entra ID. Synk.to labels them and flags the ones with risky scopes.
Risky AI scopes, explained
- Full Mail access (Critical): reads, sends and deletes every email.
- Full Drive access (Critical): reads, changes and deletes every file the user can open.
- Full Calendar access (High): reads, creates and edits every event, including private ones.
See how Synk.to scores every scope in the OAuth scope risk model.
Compare the best shadow AI detection tools, learn how to detect shadow AI, or see how an OAuth grant led to the Vercel breach. Using Claude or ChatGPT with company mail and files? See what Claude connectors and ChatGPT apps can access.

Enterprise-grade security and compliance at every step
All data is securely encrypted in transit and at rest, following the latest industry best practices.
Stay ahead of shadow AI with continuous monitoring
Maintain compliance with SOC 2, ISO 27001, HIPAA, and the NIST AI RMF while keeping your SaaS security posture strong.
Forget manual audits and spreadsheets - Synk.to brings clarity, speed, and confidence to AI governance.
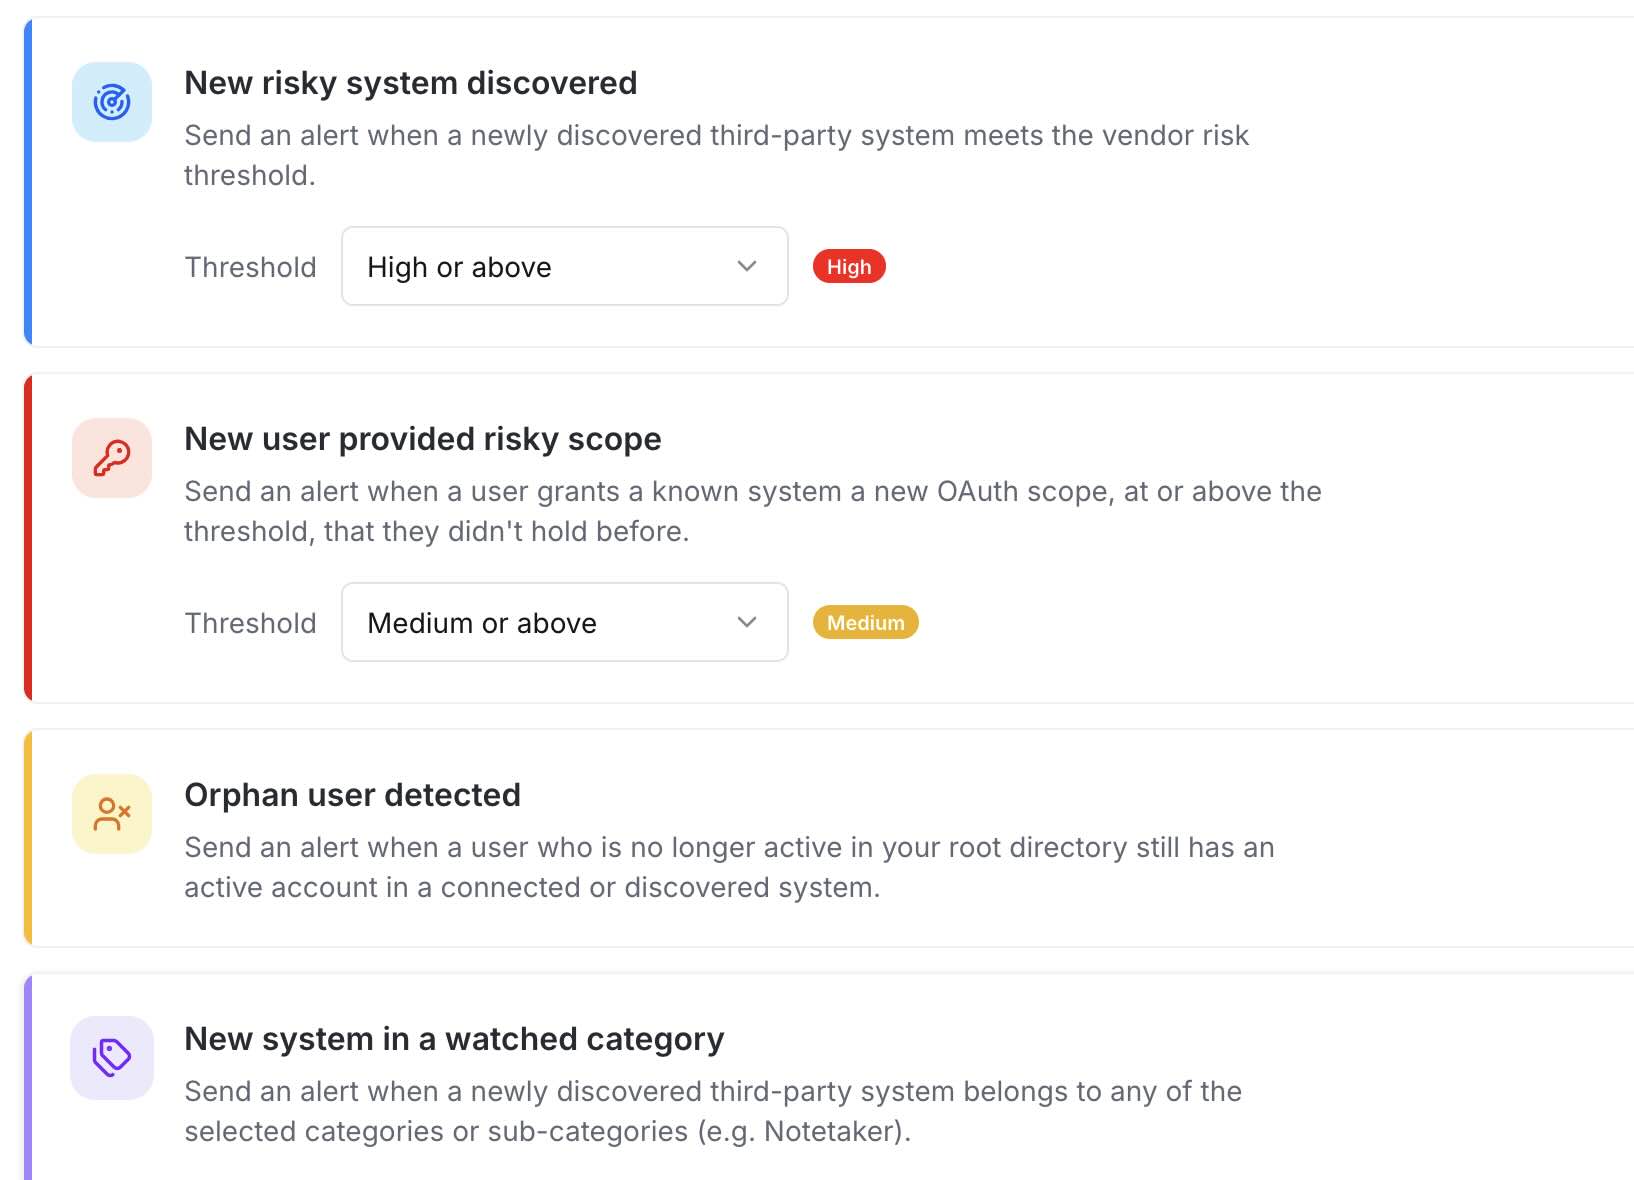
Synk.to alerts you when a New risky system discovered or New user provided risky scope event happens, so new AI grants are reviewed the day they appear.
Start small and scale only if you really need it
- Access to all features
- Connect unlimited systems
- Sync unlimited users
- Priority support
Let us tell you more. Book your slot now.
FAQs
Shadow AI detection is the process of discovering every unsanctioned AI tool, copilot, and OAuth-connected agent that touches company data — across Google Workspace, Microsoft Entra ID, Slack, Jira, Zoom and other platforms - so IT and security teams can see what AI has access to before it becomes a risk.
Synk.to connects to OAuth log of Google Workspace or Entra ID and surfaces every AI-connected app, the users who authorized it, and the scopes it was granted - flagging broad read scopes like full Mail, Drive, calendar, and meeting transcripts accesses. No manual scripts or spreadsheets required.
Yes. Synk.to doesn't require admin rights. It connects to your SaaS platforms with read-only access, so it never changes anything in your environment, and your data is encrypted in transit and at rest.
Shadow AI tools often request broad read scopes and stream sensitive data - customer calls, contracts, source code - to third-party model providers the moment they are connected. Because access is granted through OAuth, it bypasses MFA, doesn't expire, and is invisible to most DLP and CASB tooling. Synk.to makes that access visible and reviewable.
Synk.to detects AI tools and OAuth-connected agents across a wide range of SaaS applications. It has a database of 3,000+ SaaS, AI and OAuth apps, which gives you a full picture of AI access across your stack.
What is the difference between shadow AI and shadow IT?
Shadow IT is any app or service used without IT approval. Shadow AI is the subset that sends company data to AI models, such as note-takers that record calls, assistants that read mail, or agents that act on files. It needs separate attention because AI tools usually request broad read scopes and keep or process the data outside your company.
Which AI tools can Synk.to detect?
Any AI tool that connects through OAuth to Google Workspace or Microsoft Entra ID, including AI meeting note-takers, writing assistants, chat assistants and custom AI agents. Synk.to labels them as AI-related in the app inventory and flags those holding mail, file, calendar or transcript OAuth scopes.